Nice. Is this syntax supported in vyos or it needs some development?
Feed Search
Aug 15 2022
Aug 15 2022
c-po moved T4565: vlan aware bridge not working from In Progress to Finished on the VyOS 1.3 Equuleus (1.3.2) board.
c-po edited projects for T4565: vlan aware bridge not working , added: VyOS 1.3 Equuleus (1.3.2); removed VyOS 1.3 Equuleus (1.3.3).
aserkin renamed T4615: vpn sessions-columns configuration needed from vpn session-columns configuration needed to vpn sessions-columns configuration needed.
Viacheslav closed T3988: Feature Request: IPsec Multiple local/remote prefix for the tunnel as Resolved.
patrickli added a comment to T4612: Support arbitrary netmasks in firewall rules.
Viacheslav added a comment to T4612: Support arbitrary netmasks in firewall rules.
It is possible but with specific syntax
I found some examples:
nft insert rule ip filter VYOS_FW_FORWARD ip 'saddr & 0.255.0.255 != 0.11.0.13' counter
patrickli added a comment to T4612: Support arbitrary netmasks in firewall rules.
OK. I was trying to migrate from an EdgeRouter and this is a rule I used to have.
patrickli added a comment to T4611: UPnP rule IP should be a prefix instead of an address.
set service upnp rule 10 action allow
set service upnp rule 10 external-port-range 1024-65536
set service upnp rule 10 internal-port-range 1024-65536
set service upnp rule 10 ip 10.0.0.1/24
Viacheslav added a comment to T4612: Support arbitrary netmasks in firewall rules.
@patrickli nftables is not engine for iptables. It is programs to work with netfilter
That's why I ask for the real example
root@r1:/home/vyos# nft insert rule ip6 filter INPUT ip6 saddr ::dead:beef/::ffff:ffff counter
Error: syntax error, unexpected string, expecting number
insert rule ip6 filter INPUT ip6 saddr ::dead:beef/::ffff:ffff counter
                                                   ^^^^^^^^^^^
root@r1:/home/vyos#patrickli added a comment to T4612: Support arbitrary netmasks in firewall rules.
Yeah nftables is just the engine for iptables. EdgeOS supports this syntax.
Viacheslav added a comment to T4612: Support arbitrary netmasks in firewall rules.
@patrickli In 1.4 we don't use iptables, we use nftables
LInk to nftables example will be helpful.
Viacheslav added a comment to T4611: UPnP rule IP should be a prefix instead of an address.
@patrickli Could you attach an example of VyOS configuration with set service upnp xxx
If you manually change upnpd.conf does it work correctly?
Viacheslav added a comment to T4609: Unable to Restart Container VyOS 1.4.
Viacheslav changed the status of T4609: Unable to Restart Container VyOS 1.4 from Open to In progress.
Viacheslav changed the status of T4595: DPD interval and timeout do not work in DMVPN from Open to Needs testing.
Aug 14 2022
Aug 14 2022
dmbaturin edited projects for T4393: sstp: add support for configuring host-name (SNI), added: VyOS 1.3 Equuleus (1.3.3); removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4412: commit archive: reboot not working with sftp, added: VyOS 1.3 Equuleus (1.3.3); removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin closed T4421: Add support for floating point numbers in the numeric validator as Resolved.
dmbaturin edited projects for T2763: New SNMP resource request - SNMP over TCP, added: VyOS 1.3 Equuleus (1.3.3); removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4511: IPv6 DNS lookup, added: VyOS 1.3 Equuleus (1.3.3); removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4533: Radius clients don’t have simple permissions, added: VyOS 1.3 Equuleus (1.3.3); removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4565: vlan aware bridge not working , added: VyOS 1.3 Equuleus (1.3.3); removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T3474: Revisit storing syntax version of interface definitions in XML file, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin changed the status of T3785: Add unicode support to configtree backend, a subtask of T2941: Using a non-ASCII character in the description field causes UnicodeDecodeError in configsource.py, from Unknown Status to Resolved.
dmbaturin edited projects for T3988: Feature Request: IPsec Multiple local/remote prefix for the tunnel, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4094: Missed conntrack-sync failover-mechanism cluster, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4190: Add commit comment to the configuration API., added: VyOS 1.3 Equuleus (1.3.3), VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4222: Support for TWAMP as round-trip metric, added: VyOS 1.3 Equuleus (1.3.3), VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4238: Support for overriding XML properties in the template preprocessor, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin changed the status of T4260: Extend vyos.configdict.node_changed() to support recursiveness, a subtask of T4203: Reconfigure DHCP client interface causes brief outages, from Unknown Status to Resolved.
dmbaturin changed the status of T4260: Extend vyos.configdict.node_changed() to support recursiveness, a subtask of T4235: Add config tree diff algorithm, from Unknown Status to Resolved.
dmbaturin edited projects for T4291: Consolidate component version read/write functions, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4292: Rewrite vyatta-save-config.pl to Python, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4295: Use config_tree instead of legacy loadFile in vyos-load-config.py, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin edited projects for T4316: Update save-config/load-config, added: VyOS 1.4 Sagitta; removed VyOS 1.3 Equuleus (1.3.2).
dmbaturin renamed T4572: Add an option to force interface MTU to the value received from DHCP from Add an option to force interface MTU to the value received by DHCP to Add an option to force interface MTU to the value received from DHCP.
dmbaturin renamed T4572: Add an option to force interface MTU to the value received from DHCP from Remove default values in MTU nodes to Add an option to force interface MTU to the value received by DHCP.
jagekurt added a comment to T4609: Unable to Restart Container VyOS 1.4.
Great, thanks
Viacheslav added a comment to T4609: Unable to Restart Container VyOS 1.4.
It seems after this commit https://github.com/vyos/vyos-1x/commit/08cb762347208b21a8cbf81f7b35707d7e6dd4ac
I’ll take a look later
syncer edited projects for T3976: Missing prefix-list and access-list option from ipv6 route-map, added: VyOS 1.3 Equuleus (1.3.2); removed VyOS 1.3 Equuleus (1.3.0-epa3).
Aug 13 2022
Aug 13 2022
sempervictus added a comment to T4607: Configuration commit fails on kernel 5.15 (and likely others) in libboost's filesystem::copy_file from EXEDEV on the FUSE UnionFS mounts.
Got the PR working:
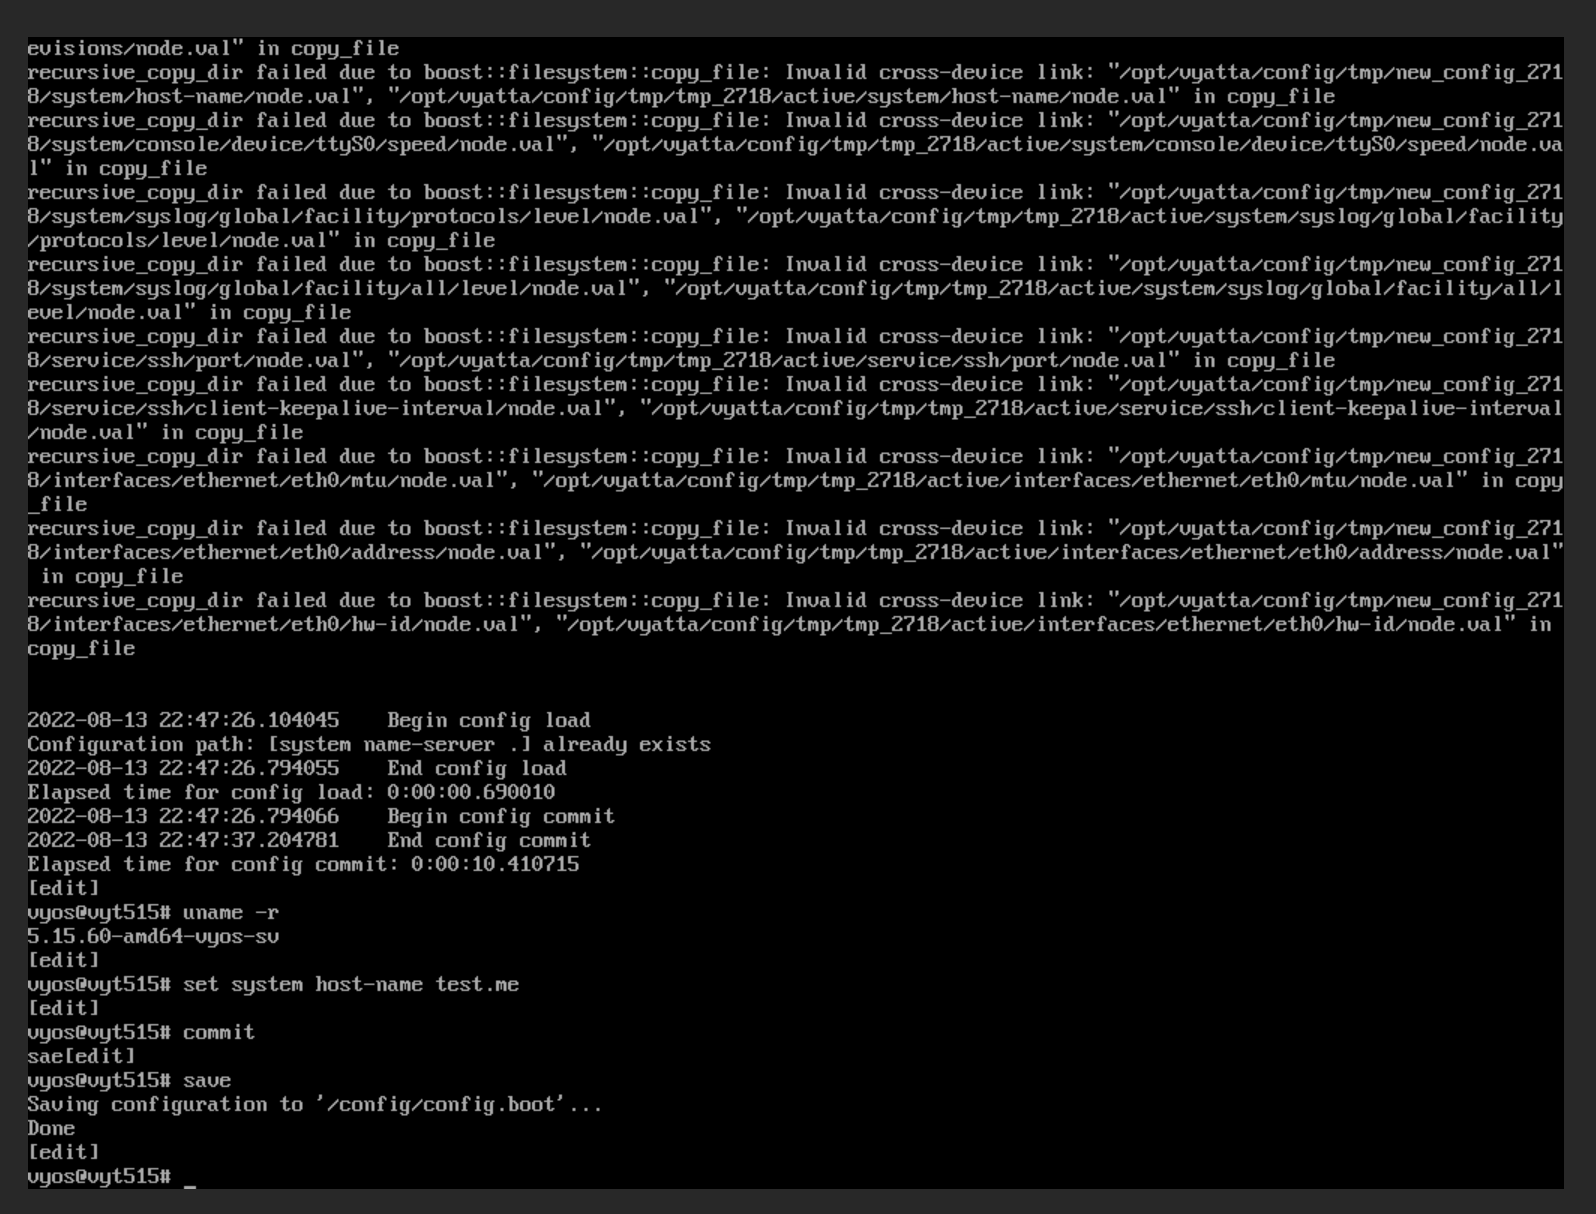
sempervictus added a comment to T4607: Configuration commit fails on kernel 5.15 (and likely others) in libboost's filesystem::copy_file from EXEDEV on the FUSE UnionFS mounts.
Using the pull requests filesystem copy, same place, new error:
vyos@vyos-515:~$ cat /var/log/vyatta/*log
cp[/opt/vyatta/config/tmp/new_config_1615]->[/opt/vyatta/config/tmp/tmp_1615/work]
cp w->tw failed[unknown exception]
cp[/opt/vyatta/config/tmp/new_config_2665]->[/opt/vyatta/config/tmp/tmp_2665/work]
cp w->tw failed[unknown exception]
vyos@vyos-515:~$ dpkg -l|grep vyatta-cfg
ii  libvyatta-cfg-dev                    0.102.0+vyos2+current5              amd64        libvyatta-cfg development package
ii  libvyatta-cfg1                       0.102.0+vyos2+current5              amd64        vyatta-cfg back-end library
ii  libvyatta-cfg1-dbgsym                0.102.0+vyos2+current5              amd64        debug symbols for libvyatta-cfg1
ii  vyatta-cfg                           0.102.0+vyos2+current5              amd64        VyOS configuration system
ii  vyatta-cfg-dbgsym                    0.102.0+vyos2+current5              amd64        debug symbols for vyatta-cfg
ii  vyatta-cfg-qos                       0.15.42+vyos2+current1              all          VyOS Qos configuration templates/scripts
ii  vyatta-cfg-system                    0.20.44+vyos2+current22             amd64        VyOS system-level configuration
vyos@vyos-515:~$ uname -r
5.15.59-amd64-vyos-sv
vyos@vyos-515:~$
If Linux maintainers backport the delta causing this to 5.10, it could become a rather pressing concern, but for now merely a show-stopper in terms of moving past 5.10LTS.
sempervictus added a comment to T4607: Configuration commit fails on kernel 5.15 (and likely others) in libboost's filesystem::copy_file from EXEDEV on the FUSE UnionFS mounts.
Created a pull request implementing a rudimentary fall-through-on-exception to standard API from the Boost version @ https://github.com/vyos/vyatta-cfg/pull/49
Have not built it yet, nor am i a formal C++ developer (hackers are informal everything developers and rarely formal anything developers), so would appreciate eyes on and sanity checks.
Exception can probably be scoped better to only trip on EXEDEV but i dont see a logical problem with falling-through like this on other errors (is this a bad assumption?).
Viacheslav added a comment to T538: Support for network mapping in NAT.
PR https://github.com/vyos/vyos-1x/pull/1466
Let me know if there is what you are expecting,
requires more tests
set nat static rule 10 destination address '10.0.1.1'
set nat static rule 10 inbound-interface 'eth0'
set nat static rule 10 translation address '192.168.1.1'
Aug 12 2022
Aug 12 2022
Viacheslav added a comment to T3670: Option to disable HTTP port 80 redirect.
@artooro Did you try listen-port option for this case?
set service https api gql
set service https api keys id KID key 'foo'
set service https api socket
set service https virtual-host foo listen-port '2580'
Check:
vyos@r14# sudo netstat -tulpn | grep nginx
tcp        0      0 0.0.0.0:2580            0.0.0.0:*               LISTEN      3570/nginx: master
tcp6       0      0 :::2580                 :::*                    LISTEN      3570/nginx: master
[edit]
vyos@r14#
Viacheslav added a comment to T4122: interface ip address config missing after upgrade from 1.2.8 to 1.3.0 (when redirect is configured?).
@n.fort Create please PR for 1.3
Aug 11 2022
Aug 11 2022
Viacheslav changed the status of T4603: Need a config option to specify NAS-IP-Address for vpn l2tp from In progress to Needs testing.
@aserkin Will be present in the next rolling release.
Viacheslav updated subscribers of T4605: Firewall change default table names.
Viacheslav updated the task description for T4605: Firewall change default table names.
Viacheslav added a comment to T4374: ipv6 address drops from interface, but network still active.
@ajgnet Could you show routes after this bug?
sudo ip -6 route show
sudo ip -6 route get 2607:f8b0:4006:80d::200e
Aug 10 2022
Aug 10 2022
Viacheslav changed the status of T4485: OpenVPN: Allow multiple CAs certificates from In progress to Needs testing.
Viacheslav added a comment to T4595: DPD interval and timeout do not work in DMVPN.
Viacheslav added a comment to T4603: Need a config option to specify NAS-IP-Address for vpn l2tp.
Viacheslav changed the status of T4603: Need a config option to specify NAS-IP-Address for vpn l2tp from Open to In progress.
m4rcu5 added a comment to T4602: DHCP `ping-check` enabled by default.
I've verified this behavior with 1.4-rolling-202207290217 and 1.4-rolling-202204250217.
Viacheslav added a comment to T4118: IPsec syntax overhaul.
aserkin added a comment to T4603: Need a config option to specify NAS-IP-Address for vpn l2tp.
Hi Viacheslav
Sorry, i probably misspelled the config option. Actually it's availabe at [radius] section of accel-ppp.conf.
Below is the [radius] section from my /run/accel-pppd/l2tp.conf after i changed
/usr/libexec/vyos/conf_mode/vpn_l2tp.py:
n.fort added a comment to T4602: DHCP `ping-check` enabled by default.
What version you are using?
Viacheslav added a project to T4603: Need a config option to specify NAS-IP-Address for vpn l2tp: VyOS 1.4 Sagitta.
Aug 9 2022
Aug 9 2022
m4rcu5 added a comment to T4602: DHCP `ping-check` enabled by default.
Allow me to proof the opposite.
n.fort added a comment to T4602: DHCP `ping-check` enabled by default.
As remarked and as expected, this option is not enable by default.
Proofs:
- Fist scenario: no ping-check option introduced in configuration:
ajgnet added a comment to T2518: Add support for IPv6 NAT (NPTv6).
Yes, would be great to fully support dynamic prefix when the prefix is not known
Viacheslav added a comment to T4547: Show vpn ipsec sa show unexpected prefix 'B' in packets.
Will be fixed in https://github.com/vyos/vyos-1x/pull/1458
n.fort changed the status of T4598: nat66 - Add exclude options, a subtask of T2518: Add support for IPv6 NAT (NPTv6), from In progress to Needs testing.
Aug 8 2022
Aug 8 2022
Viacheslav added a comment to T4602: DHCP `ping-check` enabled by default.
ping-check shouldn't be allowed by default
To enable it you have to set set service dhcp-server shared-network-name Lan01 ping-check
There is no configuration in generated .conf:
vyos@r14# cat /run/dhcp-server/dhcpd.conf | grep ping
[edit]
vyos@r14#
n.fort added a subtask for T2518: Add support for IPv6 NAT (NPTv6): T4598: nat66 - Add exclude options.
n.fort added a parent task for T4598: nat66 - Add exclude options: T2518: Add support for IPv6 NAT (NPTv6).
a.apostoliuk added a comment to T4537: MACsec not working with cipher gcm-aes-256.
I have tested macsec with gcm-aes-256. It works. (1.4-rolling-202208080217)
a.apostoliuk added a comment to T4538: Macsec does not work correctly when the interface status changes..
I have tested on 1.4-rolling-202208080217.
The first problem was fixed.
The second problem is not fixed
Viacheslav closed T4586: Add to NAT66: SNAT destination address and DNAT source address. as Resolved.
Aug 7 2022
Aug 7 2022
Unknown Object (User) created T4601: dhcp : relay agent IP address issue..
RyVolodya added a comment to T4598: nat66 - Add exclude options.
Hello, This functionality for nat66 is described here:
https://phabricator.vyos.net/T4586
Aug 6 2022
Aug 6 2022
jack9603301 added a comment to T4598: nat66 - Add exclude options.
hi, you can set this to a subtask of my task