Jun 10 2022
Fix Regex for addresses and python ckecks https://github.com/vyos/vyos-1x/pull/1354
- Some domains can't be added, for example dns.google
vyos@r12# set firewall group domain-group DOMAINS address dns.google
Fix smoketest https://github.com/vyos/vyos-1x/pull/1352
Jun 9 2022
From provided log syntax error in config string 6
‘holding-time 300’
Jun 8 2022
Jun 7 2022
Jun 5 2022
Added more options. PR https://github.com/vyos/vyos-1x/pull/1350
I already merged your XML definition ;)
I once made XML, it might come in handy
Jun 4 2022
Ultimately I moved my physical connection from port eth0 to eth4, and configured eth4 with the same config as was on eth0. Once I did that everything was stable and has been stable for days (nearly a week now). I'm not sure what could be causing an interface to work for an amount of time, then as if on-cue stop forwarding packets.
Jun 3 2022
Should I make improvements to the remaining revisions in the PR?
Sorry I just saw it now, I'll test it. But because of limited conditions, I may test in the future, please forgive me
Jun 2 2022
@m.korobeinikov I believe that I already posted this some time ago, but just in case...
Not all combinations of DPD and close-action are safe. Actually, most of them sooner or later will lead to issues with IPSec. So, I created the next scheme. It is from 2020, so I will not say that nothing was changed from that time, however, it shows well how careful you should be while configuring IPSec. On the scheme, you can see the only safe configuration of the close-action option, depending on how the peer is configured, but the same logic can be applied to DPD.
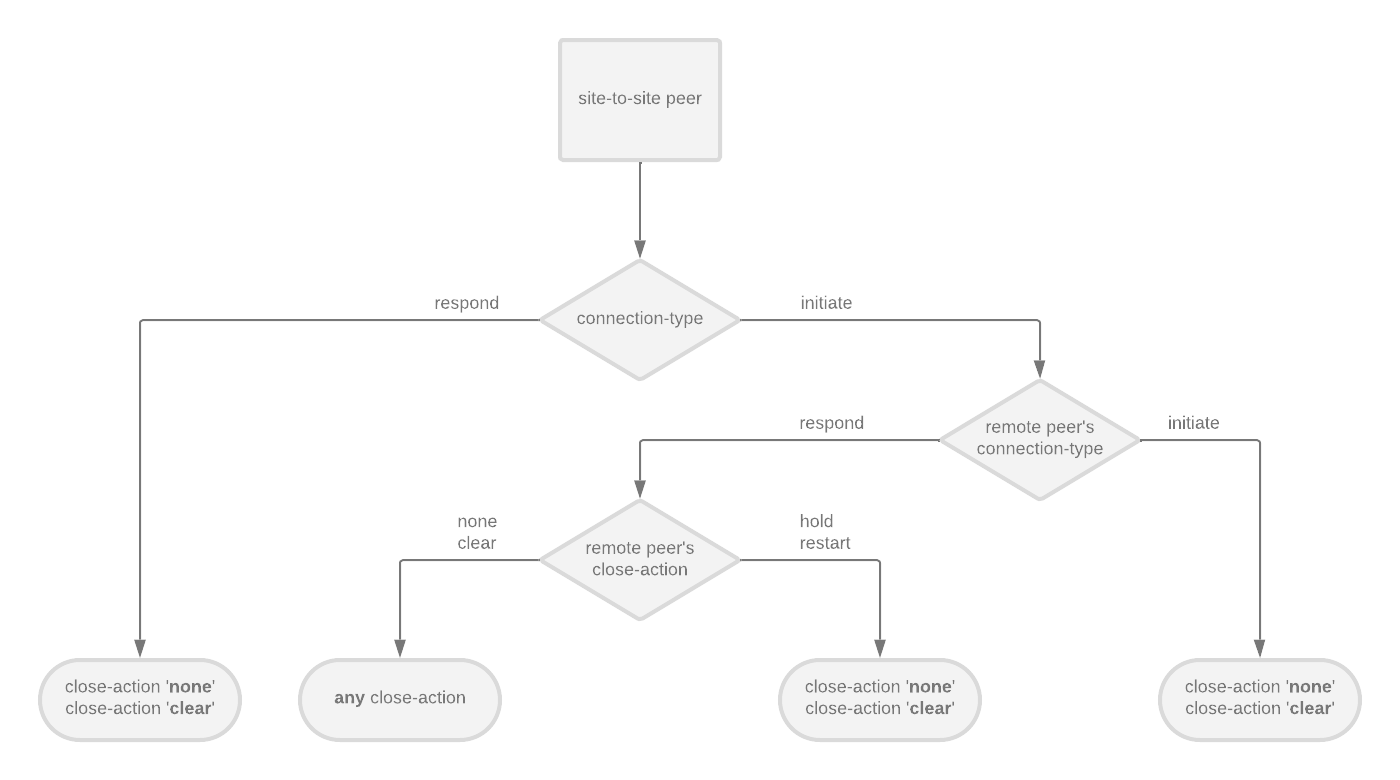
PR https://github.com/vyos/vyos-build/pull/240
disable owamp|twamp.service by default
@SrividyaA will be present in the next rolling release
PR for the current https://github.com/vyos/vyos-1x/pull/1346
For Debian11 requires pkg "libpam-tacplus" that is not available https://github.com/kravietz/pam_tacplus/issues/180
Jun 1 2022
May 31 2022
Yes on this version it is available the requested options for ipv6:
yes, it was added on this version vyos-1.4-rolling-202205311706, please check again
I just check and on version: vyos-1.4-rolling-202205310217 is still missing :(
We've added this feature in our latest nightly building release, could you check it ?
May 30 2022
PR for op-mode importing existing PKI files into config: https://github.com/vyos/vyos-1x/pull/1343
May 29 2022
Currently dealing with some minor FRR issues:
May 28 2022
@fernando Could you try to set sysctl mark?
sysctl -w net.ipv4.conf.eth0.src_valid_mark=1
sysctl -w net.ipv4.conf.eth1.src_valid_mark=1
PR https://github.com/vyos/vyos-1x/pull/1340
set service event-handler event first filter pattern '.*ssh2.*'
set service event-handler event first script arguments '192.0.2.5'
set service event-handler event first script environment interface value 'eth0'
set service event-handler event first script path '/config/scripts/hello.sh'